Selecting dependable managed cyber security services kenya enterprises can trust requires moving past generic sales promises and marketing checklists. IT directors and operational leaders must evaluate continuous telemetry ingestion, proactive incident containment, and measurable service level agreements. This buyer’s guide provides an enterprise evaluation framework to help you assess vendor architectures, regulatory compliance, and operational resilience.
Key takeaways
- True security operations center (SOC) delivery is defined by mean time to respond (MTTR) rather than passive ticket dispatching.
- Integrated endpoint detection and response (EDR) coupled with next-generation firewalls forms the baseline for modern perimeter defence.
- Data sovereignty and incident notification windows require strict alignment with the Kenya Data Protection Act alongside global standards.
- Co-managed models allow existing internal teams to retain policy governance while outsourcing round-the-clock monitoring and tier-three threat hunting.
The Evolving Threat Landscape for East African Enterprises
Enterprise perimeters across East Africa face sophisticated, automated risks that easily bypass traditional antivirus tools. Threat actors now leverage automated scripts and machine learning frameworks to conduct automated reconnaissance on exposed infrastructure. As reported by Dark Reading, security researchers observed threat actors turning Artex, an AI pen-testing tool, into a weapon to automate offensive operations. Consequently, basic firewalls without continuous threat inspection leave corporate cloud applications and communications systems severely vulnerable.
Targeted ransomware campaigns frequently gain initial access via phishing or unpatched edge network appliances. Once inside, attackers move laterally across internal networks to compromise file repositories and backup controllers. Writing on digital risk management, Financier Worldwide highlighted how high-reliability industries are shifting focus from mere regulatory compliance to comprehensive operational resilience. To achieve that level of resilience, the investment in cyber security services kenya organisations procure must shift from reactive break-fix support to proactive threat mitigation.
Core Technical Architecture for Managed Cyber Security Services Kenya
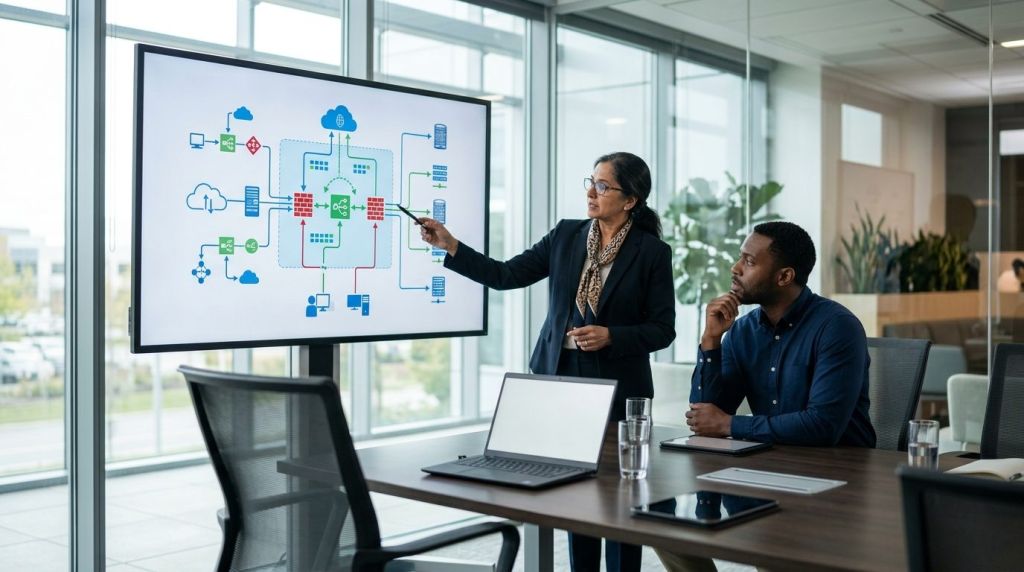
A dependable enterprise managed defence architecture operates across multiple synchronized security layers. Standalone security tools create visibility silos that prevent rapid cross-correlation of abnormal network activity. Therefore, leading providers engineer environments that link perimeter firewalls, cloud infrastructure, and endpoint telemetry into a consolidated monitoring framework.
At the network edge, next-generation firewall engineering is essential. Purpose-built hardware appliances, such as those covered in our Fortinet firewall buyer’s guide, perform deep packet inspection, automated intrusion prevention, and application filtering without bottlenecking enterprise bandwidth. These appliances must integrate directly with software-defined wide area network (SD-WAN) fabrics to secure branch office links and hybrid cloud tunnels.
Simultaneously, host-level protection requires advanced behaviour analysis and exploit mitigation. Implementing a modern Sophos endpoint security architecture ensures that zero-day ransomware execution is halted before payload encryption starts. Integrated managed detection and response (MDR) services enable analysts to roll back malicious file alterations and isolate compromised devices instantaneously.
Vetting SOC Architecture and SOC as a Service SLA Metrics
Many prospective buyers struggle to differentiate between a genuine SOC and an alerting relay service. A basic monitoring service merely forwards vendor alerts to your inbox, placing the remediation burden back onto your internal team. Conversely, an enterprise SOC as a service SLA guarantees active containment, deep forensic investigation, and definitive incident eradication around the clock.
When evaluating managed cyber security services kenya providers offer, scrutinise their telemetry pipelines and performance metrics. Ask potential partners how they calculate Mean Time to Detect (MTTD) versus Mean Time to Respond (MTTR). The following operational thresholds represent the enterprise standard for mature security operations:
| Metric | Alert Forwarding Relay | Enterprise Managed SOC Standard |
|---|---|---|
| Telemetry Coverage | Business hours only (8×5) | Continuous 24/7/365 coverage across holidays |
| Mean Time to Detect (MTTD) | Several hours to days | Under 15 minutes for confirmed critical anomalies |
| Mean Time to Respond (MTTR) | Not covered (internal IT action) | Under 30 minutes for active containment |
| Incident Containment | Manual email advice | Automated host isolation and dynamic firewall blocking |
| Root Cause Analysis | Rarely provided | Comprehensive timeline, IOC export, and debrief |
Ensure the provider has established weekend escalation protocols and dedicated level-two and level-three incident responders. A service level agreement that lacks financial penalties or clear mitigation commitments provides little operational assurance during a targeted breach.
East Africa Data Protection Act Compliance and Global Governance
Regulatory compliance is no longer just an administrative box-ticking exercise. The Kenya Data Protection Act (KDPA) imposes strict operational guidelines on how data controllers and processors capture, transmit, and store personal information. In the event of a significant security incident, organizations must notify the Office of the Data Protection Commissioner within tight statutory deadlines.
Your service provider must maintain technical controls that actively support compliance requirements. This involves ensuring system logs remain immutable, maintaining secure data storage within regional boundaries where necessary, and implementing cryptographic isolation. Mature providers align their management workflows with the ISO/IEC 27001 standard to provide verifiable process maturity and risk assessment controls.
Furthermore, providers supporting cross-border enterprises should align security telemetry and incident reporting frameworks with the NIST Cybersecurity Framework. This global standardisation ensures your internal compliance reports satisfy multinational enterprise audits, insurers, and external regulatory bodies alike.
Deployment Models: Co-Managed vs. Fully Managed Defence
When engaging managed cyber security services kenya businesses frequently debate between co-managed security architectures and fully outsourced models. Neither model is inherently superior; the right choice depends on your internal technical maturity, existing headcount, and strategic division of responsibilities.
A co-managed model suits enterprises with capable internal IT personnel who lack dedicated threat-hunting tools and round-the-clock shift coverage. In this setup, internal engineers maintain daily administrative control over directory services and user privileges. The external security partner manages the underlying detection stack, ingests raw system telemetry, and intervenes directly during critical security anomalies.
In contrast, fully outsourced managed defence delivers a complete operational package for mid-market firms without dedicated information security staff. The managed security partner assumes direct accountability for policy hardening, continuous patch verification, perimeter firewall management, and incident response. This turnkey approach provides predictable operational expenditure while eliminating the overhead of retaining scarce, specialised cybersecurity talent.
Enterprise RFP Evaluation Checklist and Critical Red Flags
Procurement teams must carefully vet technical proposals to expose operational weaknesses before signing long-term contracts. Use this structured evaluation checklist when reviewing tenders for modern managed cyber security services kenya vendors submit:
- Telemetry Storage and Segregation: Does the provider store your operational logs in dedicated, multi-tenant isolated repositories with strict role-based access?
- Log Retention Periods: Can the ingestion platform retain hot, searchable logs for at least ninety days and cold archival storage for a full year?
- Engineering Credentials: Do the assigned SOC analysts hold industry certifications such as CISSP, CISM, or vendor-specific expert credentials?
- Exit Strategy and Data Portability: Does the contract guarantee immediate export of historical security logs and configuration states if the service concludes?
- Proactive Hardening: Does the service include recurring vulnerability assessments, firewall rulebase sanitisation, and external posture reviews?
Watch out for critical warning signs during vendor presentations. If a provider relies on shared administrative credentials across client environments, dismiss their proposal immediately. Other major red flags include unmonitored default configurations on network hardware, vague incident response guarantees, and an inability to supply a live demonstration of active host isolation.
Evaluating Long-Term Operational Continuity
Resilient cyber defence requires consistent execution, ongoing configuration tuning, and deep integration with daily business workflows. Deploying top-tier hardware without experienced operational management creates a false sense of safety that evaporates under targeted attack. Organizations seeking reliable technical governance often pair cyber defence with wider managed IT support to maintain unified accountability across all systems.
By conducting a methodical partner evaluation, IT directors protect their core network assets, maintain strict regulatory compliance, and guarantee operational continuity. Call Experts engineers pragmatic, layered defence architectures designed around measurable containment outcomes rather than passive monitoring. To discuss tailored enterprise architectures, visit our contact page to consult with our enterprise infrastructure team.
Frequently asked questions
What is the typical onboarding timeline for managed cyber security services?
Standard enterprise onboarding takes two to four weeks. This period covers endpoint agent deployment, firewall configuration audits, telemetry ingestion setup, baseline behavioural tuning, and establishing formal escalation paths tailored to your organizational workflows.
How do managed security services support Kenya Data Protection Act compliance?
Managed security services support compliance by maintaining tamper-evident audit logs, enforcing data encryption, implementing strict access governance, and delivering rapid incident containment capabilities necessary to meet mandatory regulatory breach notification timelines.
What is the difference between an IT helpdesk and a managed SOC?
An IT helpdesk resolves general end-user software, hardware, and operational requests. A managed SOC focuses entirely on identifying, analysing, and neutralizing malicious activity, monitoring deep security telemetry across endpoints, servers, and perimeter networks around the clock.
Can our internal IT department retain administrative control in a co-managed model?
Yes. In a co-managed framework, your internal IT team retains operational control over local user accounts, permissions, and internal systems, while the managed security provider delivers continuous threat hunting, log analysis, and emergency incident containment.
Sources
- Artex: The AI Pen-Test Tool Hackers Turned Into a Weapon — Dark Reading, 2026-11-10
- Compliance to resilience: lessons from high-reliability industries on managing digital risk — Financier Worldwide, 2026-11-10